Ilyes Litim, DevOps & CI/CD engineer in Montréal
I automate how your infrastructure is delivered and run.
More than 7 years of experience in infrastructure, containers and CI/CD, including three years as the only DevOps engineer of a SaaS platform: multi-environment Kubernetes, GitLab CI/CD pipelines, observability.
Available for your DevOps / SRE contracts and projects · Montréal
- validatepinned versions, tests, secrets, manifests15 s
- buildstatic Next.js, nginx image1 min 38
- scanTrivy: no fixable HIGH or CRITICAL flaw27 s
- deployKubernetes, no downtime44 s
- verifypages, CSP, contact10 s
Measured when this version went live.3 min 25
Five live projects, designed and built on my own
My product and my Kubernetes projects. Everything is live, go ahead and click.
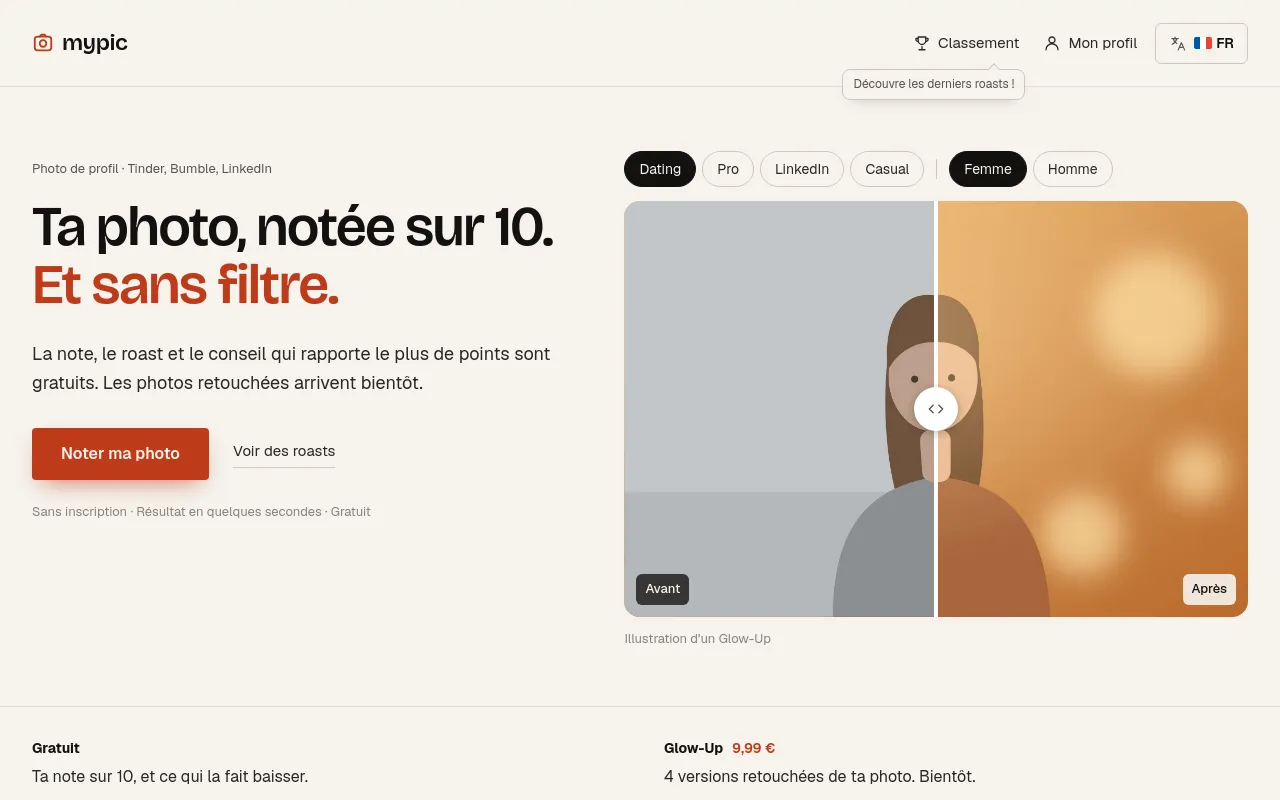 mypicmypic.hoortrend.comYou send a profile photo, the AI rates it out of 10, roasts it and tells you what to change.
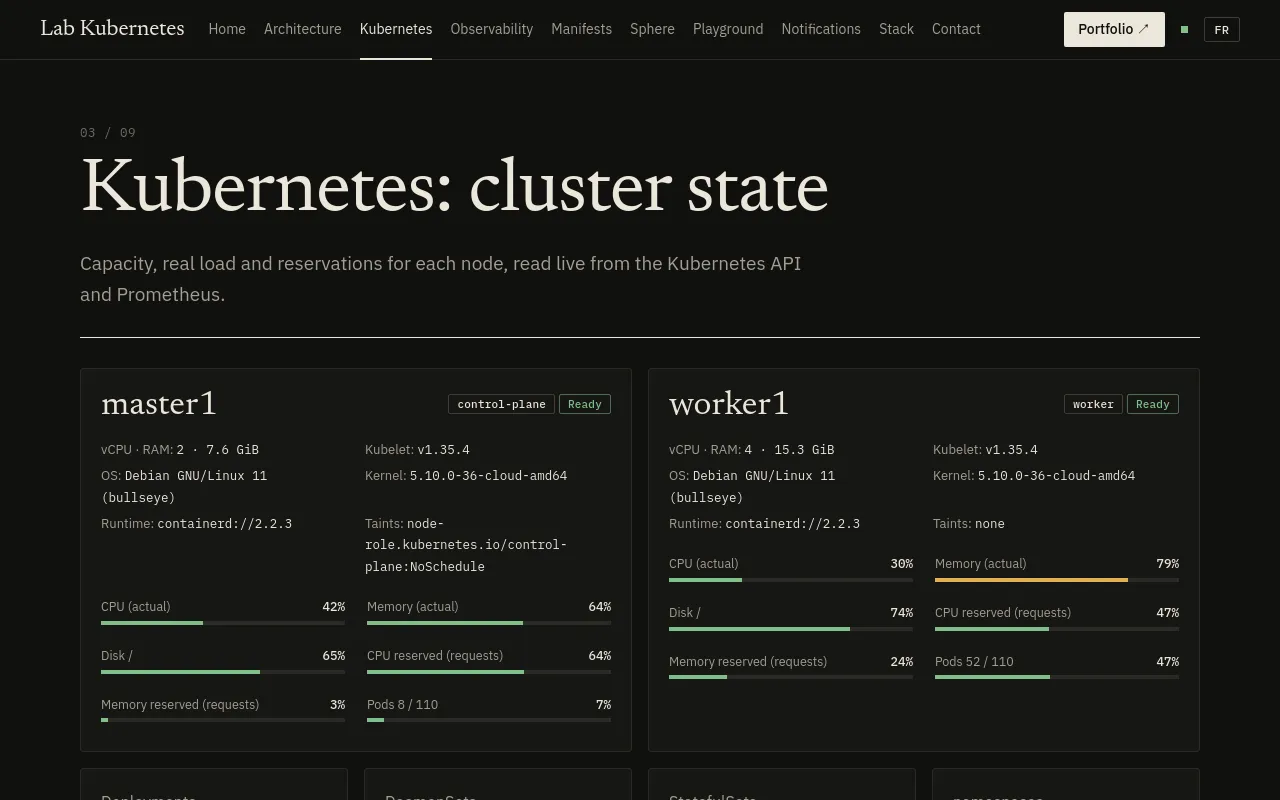 A Kubernetes cluster built and run on my ownlab.hoortrend.comTwo machines, Kubernetes built on my own: HTTPS, Git forge, monitoring, verified backups.
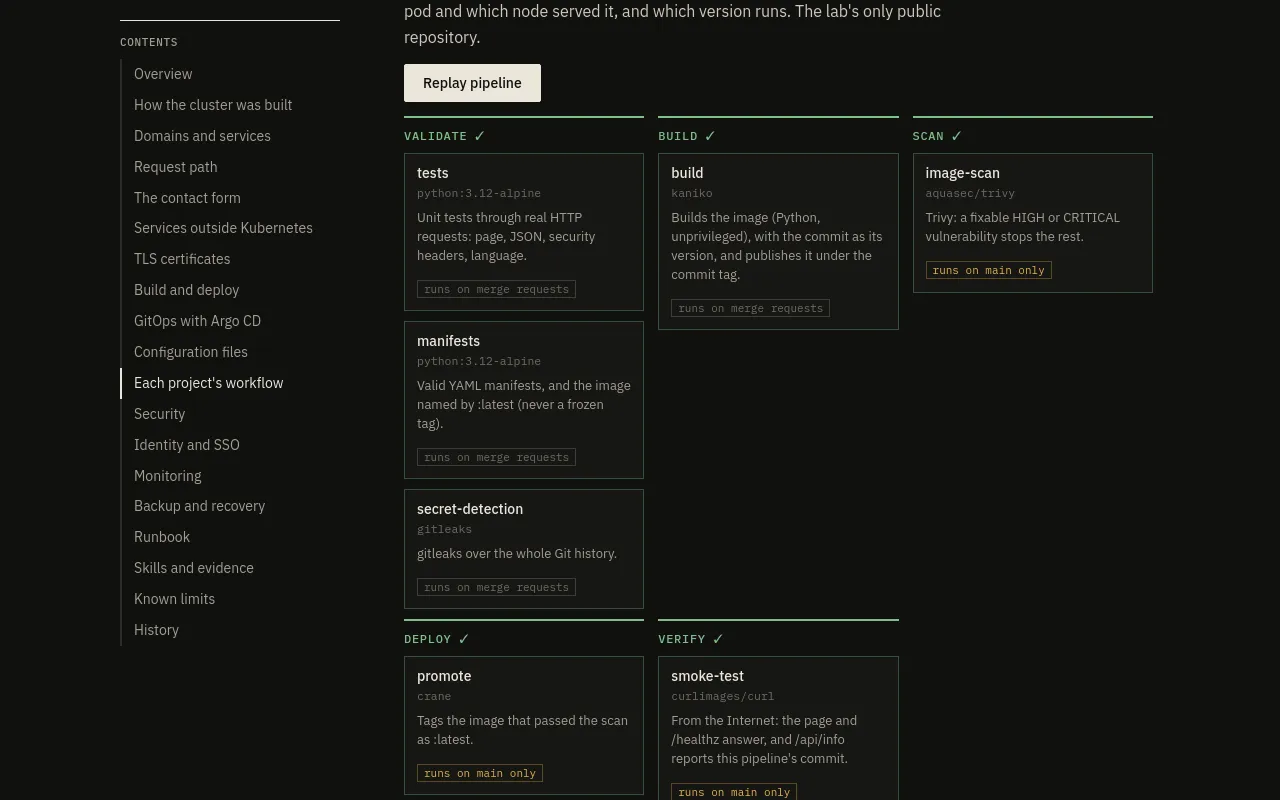 No image goes live unscanneddemo.hoortrend.comEvery app's pipeline: unprivileged build, Trivy scan, deployment, smoke test.
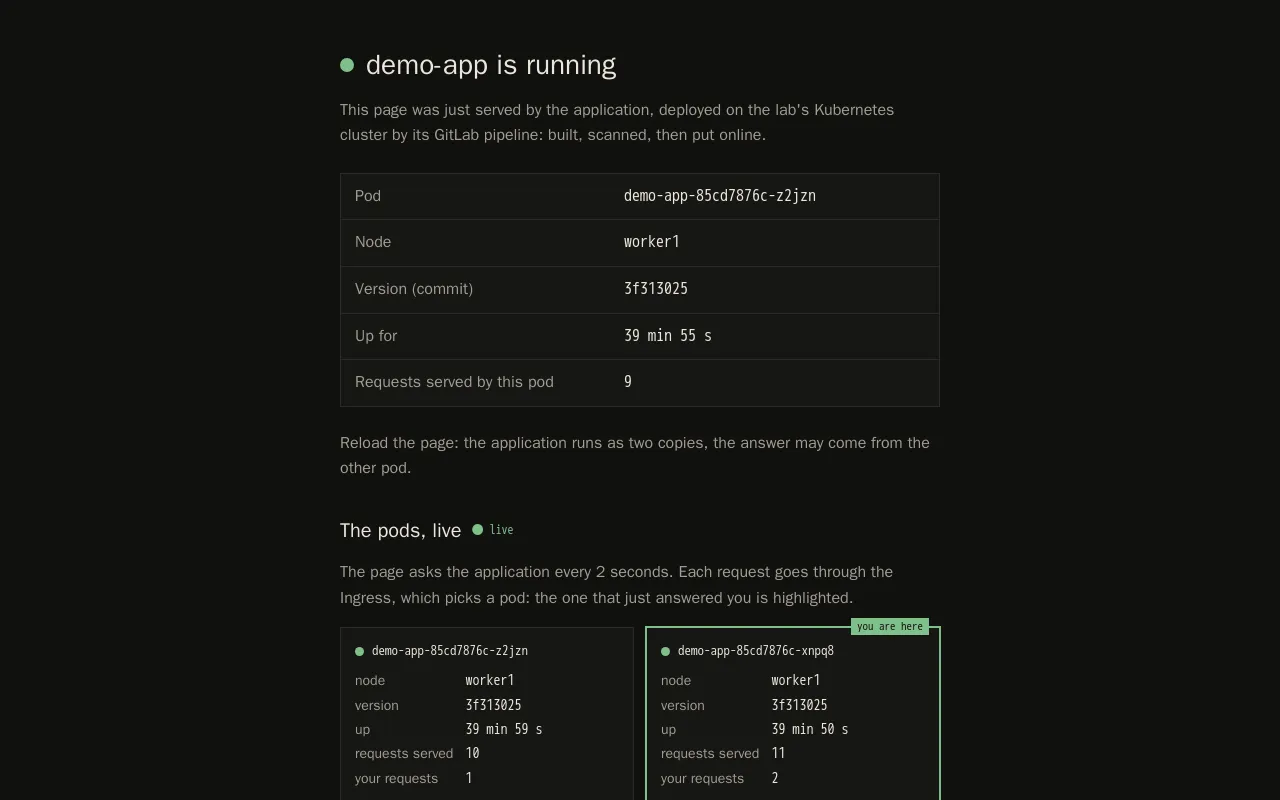 Git as the single source of truthhoortrend.com/docsArgo CD applies the repository and undoes any change made by hand on the cluster.
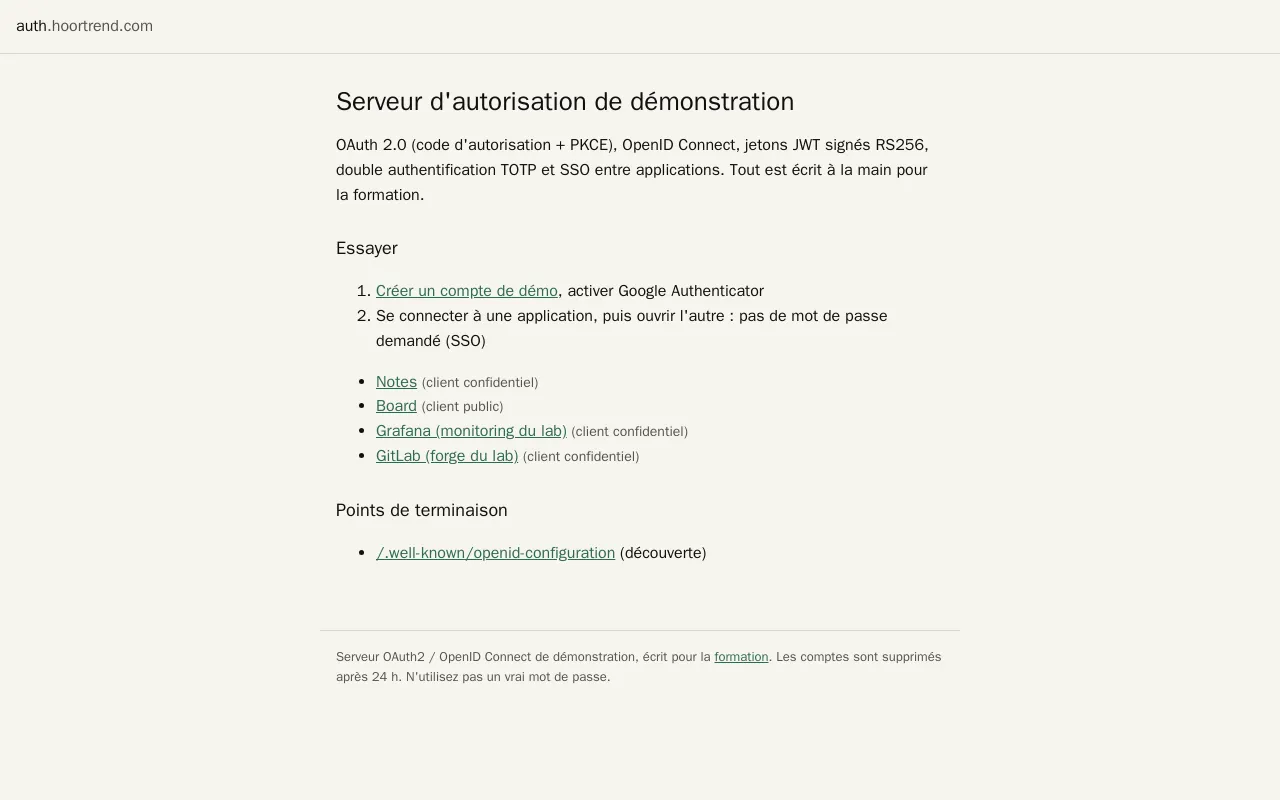 An identity provider written by handauth.hoortrend.comAn OAuth 2.0 / OpenID Connect server written by hand, providing SSO for Grafana and GitLab.
What I can do for you
- Kubernetes and containers
Clusters built, secured and run
DEV, TEST, PREPROD and PROD Kubernetes clusters installed with Kubespray and maintained: upgrades, HPA and VPA, rolling and canary deployments (Hoortrade).
Already done: Cluster installed with Kubespray, Calico, ingress-nginx, cert-manager; RBAC, NetworkPolicy, Pod Security "restricted". See the project →
- CI/CD and GitOps
Pipelines that block what must be blocked
End-to-end GitLab CI/CD pipelines (build, test, deploy) and full GitLab administration: access, branching, code review (Hoortrade).
Already done: Unprivileged Kaniko builds, blocking Trivy scan, promotion after the scan, verified deploys; Argo CD. See the project →
- Monitoring and alerting
Monitor the infrastructure, alert in time
Prometheus, Grafana (dashboards and business alerts) and Zabbix across the platform; production incidents and root cause analyses (Hoortrade).
Already done: kube-prometheus-stack, alert rules written for the lab, alerts by e-mail, an alert when a backup is missing. See the project →
- Automation
Automate what repeats
Provisioning and configuration with Terraform and Ansible (Hoortrade), Bash deployment scripts (Utopiascript), scripted Fortinet configuration (Econocom).
Already done: Helm with versioned values, backups by a versioned script and a systemd timer. See the project →
- Systems, networks, security
Solid foundations: systems, networks, security
Migration of more than 300 servers to Windows Server 2019 with no major outage (Enedis); Fortinet network security in critical infrastructure (EDF); TLS certificates and cert-manager (Hoortrade).
Already done: Worker firewall, automated TLS, an OAuth 2.0 / OpenID Connect server with its attack tests. See the project →
Evidence, not labels
Measured on my live projects and documented in public.
From systems to DevOps
- Hoortrade (Casanoov, Cazeboo, Sicaan) · FranceDevOps CI/CD Engineer2022 - 2025
- Econocom, client EDF · FranceCybersecurity Engineer2021 - 2022
- Expectra, client Enedis · FranceSystems Administration Engineer2019 - 2020
- Utopiascript · FranceSystems and Network Administration Engineer2018 - 2019
A DevOps / SRE project or contract?
Describe the need in a few lines. I answer myself, by e-mail.
Send a message