← All projects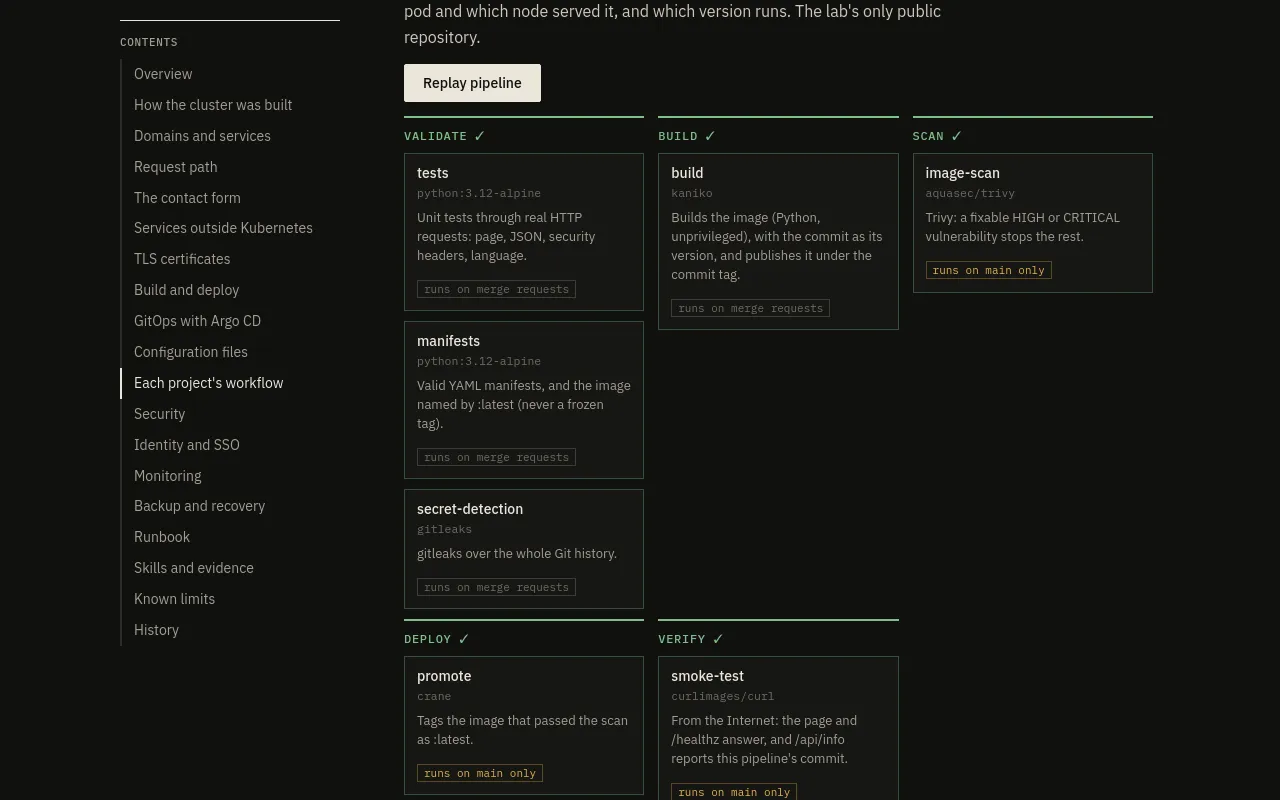
Continuous delivery · DevSecOps
No image goes live unscanned
The same GitLab CI pipeline for every application of the lab: build without privileges, scan, promote, deploy, verify. A fixable vulnerability blocks the release.
- GitLab CI
- Kaniko
- Trivy
- gitleaks
- kubectl
- RBAC
The problem
An image can go live with a known vulnerability, and an over-powered deployment account is an open door to the whole cluster.
What I built
- Branch, merge request, required pipeline: a merge is blocked until the pipeline has passed.
- Builds with Kaniko in a pod of the Kubernetes runner, with no privileged access; the image is pushed under the commit tag.
- Trivy blocks the rest on a fixable HIGH or CRITICAL vulnerability. The :latest tag is only set after the scan.
- Deployment with kubectl set image, wait for the rolling update, then a smoke test on the public site. For the demo application, the version served must be the commit's.
- gitleaks scans the whole Git history in every pipeline: a committed secret, even one deleted later, fails it.
Choices and reasons
- The CI service account may only change the image of one named Deployment: no cluster administration rights.
- A Trivy exception carries its reason and an expiry date: after that date the scan fails again and the decision must be made again.
- maxUnavailable set to 0: a new pod must be ready before an old one stops, the site stays up during an update.
Checked
- First scan: three HIGH vulnerabilities in a Python dependency (starlette), fixed before the scan was made blocking.
- The kubectl image used for deployments went from 26 fixable HIGH vulnerabilities to a few IDs with no published fix, accepted for a limited time.
- This site goes through the same pipeline: Next.js exported as static files, an unprivileged nginx image, scanned before it is deployed.
Limits and next steps
Images are not signed yet, and the cluster checks nothing at admission (signature, allowed registry). That is the planned next step: SBOM, cosign signatures, Kyverno policies, canary releases with automatic rollback. Only the demo application's repository is public.